
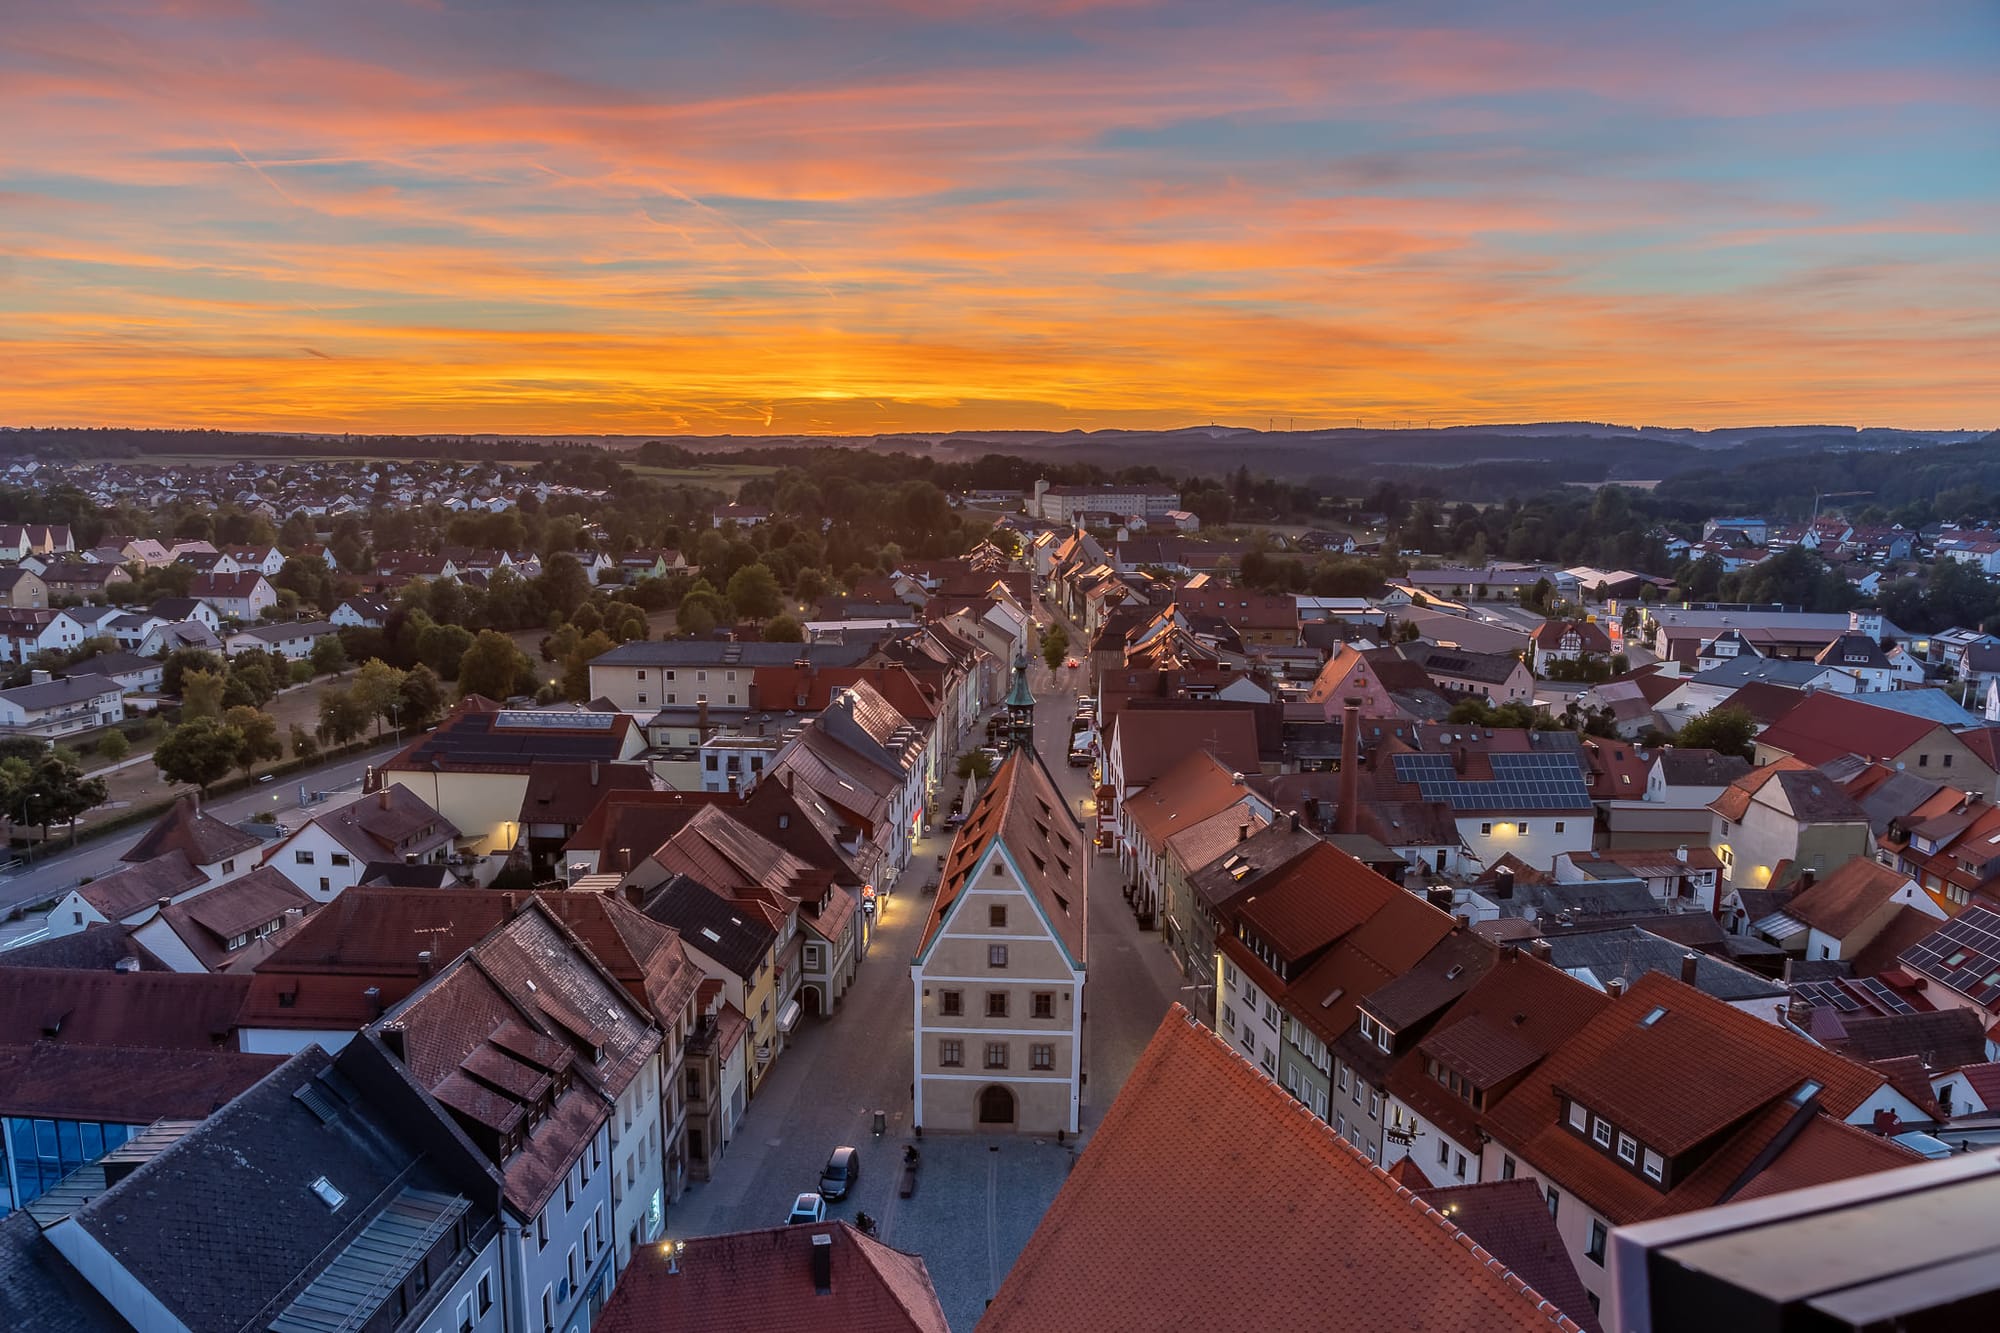
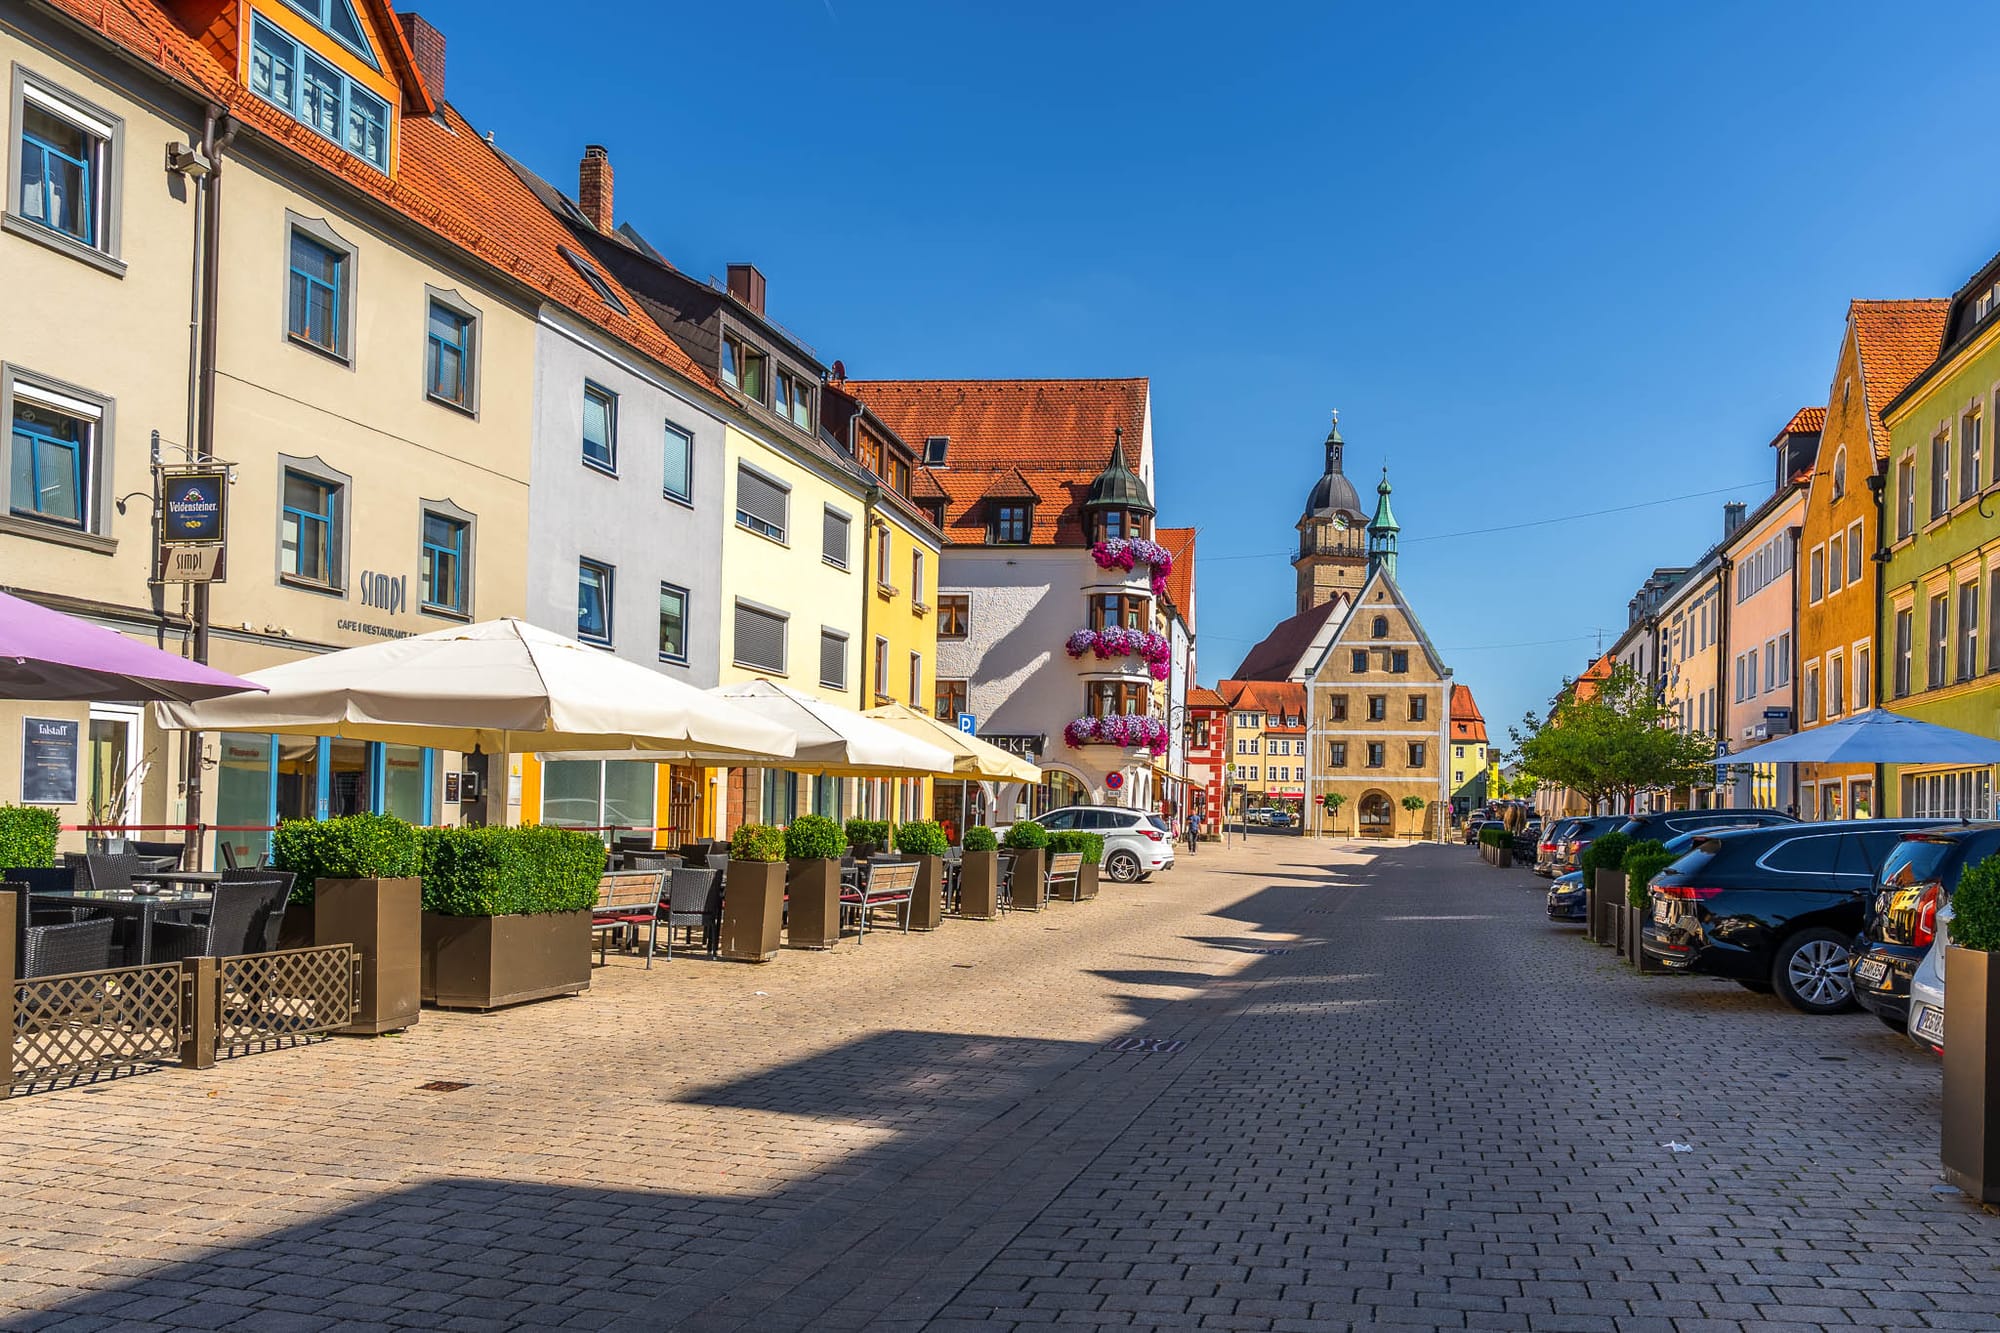
Auerbach in der Oberpfalz is a small town of 9,470 residents in Bavaria's Upper Palatinate region, in the Amberg-Sulzbach district. The town carries a working, industrial history alongside its historic market square: iron ore was mined here for centuries, and that legacy is still visible in its character today. The former Maffei mine site still has its winding towers standing, and the site now hosts a mining museum and a recurring cultural festival.
The practical approach carries over into local governance: the municipality earned Fairtrade Town status in 2024, renewed it in 2026, and takes the same sustainability-minded, accountability-driven stance across its other initiatives.
The same logic applies to IT. Managing critical infrastructure means retaining control over core processes, including how credentials are secured. Auerbach's system administration team chose a self-hosted platform with zero-knowledge encryption, combining strict access control with full sovereignty over sensitive data.
Location: Bavaria, Germany
Industry: City administration
Company size: 230+ employees
The challenge: File-based architecture became a security liability
A team of system administrators manages Auerbach's IT infrastructure. Before Passwork, the team relied on two separate open-source password managers built on the same underlying database format — one browser-based, the other a desktop application — splitting credential storage between them.
Both tools relied on a single file-based architecture, where all credentials live in one encrypted file shared across the team — a model unsuited to the sensitive, multi-user access needs of municipal IT. This caused sync failures and file-locking conflicts, requiring manual oversight of write access, and left a bigger gap: no role-based permissions and no granular access control.
Sharing the vault file over insecure channels created two risks:
- A database file sent by email or stored on an unencrypted shared drive is a single point of failure if intercepted.
- Without a centralized source of truth, outdated credential copies could stay in circulation, so someone might unknowingly use a password that had already been rotated.
For a government IT team managing access to core infrastructure, this is the kind of exposure that security frameworks are designed to prevent.
Solution: Passwork matched Auerbach's security and consistency priorities
Auerbach's search centered on two priorities: data security and credential consistency across a centralized database, rather than a set of loosely synced files. Passwork's interface, designed for system administrators and structured team collaboration rather than individual consumer use, was the first reason to consider it.
The deciding factor for starting a trial was the vendor's documented security architecture: zero-knowledge encryption that the team could verify before committing.
What Auerbach needed from a new solution
Auerbach's security and consistency priorities required three specific architectural features: on-premise deployment, client-side encryption, and a data structure that could scale with the municipality's infrastructure. Each addressed a specific limitation of the team's previous file-based setup.
- Self-hosted, on-premise deployment for full control over sensitive data on the municipality's own servers
- Zero-knowledge encryption to eliminate server-side exposure of credentials and encryption keys
- Vault and folder structure to organize access by infrastructure component or client system
Zero-knowledge encryption means the server never has access to unencrypted data or the encryption keys. Data is encrypted client-side before it is transmitted or stored. An administrator or attacker with full server access sees only ciphertext. For a public sector body handling credentials to core network infrastructure, this removes an entire category of server-side breach risk.
Technical integration
Deployment ran through Docker, letting the team stand up a working instance quickly and test it against real infrastructure credentials instead of a demo dataset. Migration from the team's existing databases went through Passwork's import interface without errors. The fast test deployment and clean migration let the team move from evaluation to production quickly.
Results: From static files to a real-time, centralized system
Auerbach retired its file-based vaults for a centralized system that updates in real time across the team. Credentials are now rotated and versioned centrally, removing the stale-copy risk of the previous solutions. The team also reported time savings from Passwork's browser extension in daily infrastructure work.
| Aspect | Previous solutions | Passwork |
|---|---|---|
| Storage model | File-based, manually synced | Centralized database, updated in real time |
| Access control | No role-based permissions | Granular, role-based access |
| Encryption | Local file encryption | Zero-knowledge, client-side encryption |
| Credential sharing | Manual file transfer over insecure channels | Instant sharing, with every access logged |
| Version tracking | Risk of outdated copies in circulation | Full history of every password change |
"In modern IT administration, password management shouldn’t be
a bottleneck. Passwork gave us back the flexibility and security we
were missing with static file-based vaults." — Stadt Auerbach systems administration team
Auerbach's evaluation centered on a specific security gap: encrypting and controlling access to credentials for critical infrastructure systems. Encryption architecture and granular access control carried equal weight with daily usability — the team needed a system secure enough for sensitive access, but simple enough to run department-wide without a learning curve.
Conclusion
Auerbach's migration shows that single file-based password tools reach their limit not at the point where access control and audit requirements outgrow what a shared file can provide. A team managing critical municipal infrastructure faces the same exposure as a large enterprise once credentials are shared without role-based permissions or a single source of truth. Passwork closed that gap for Auerbach with a centralized, zero-knowledge architecture.
"With Passwork, we can work seamlessly as a team, keep strong
performance in our daily tasks, and maintain full control within our own
infrastructure." — Stadt Auerbach systems administration team
 Passwork Team
 Passwork Team
 Alex Muntyan
Table of contents
Table of contents

Self-hosted password manager for business
Passwork provides an advantage of effective teamwork with corporate passwords in a totally safe environment. Double encryption and zero-knowledge architecture ensure your passwords never leave your infrastructure.
Learn more